When a healthcare system, a bank, or a government contractor deploys Power BI, the stakes around security are categorically different from a retail company tracking store traffic. Patient health records, cardholder data, personally identifiable information, and financial disclosures are subject to strict regulatory frameworks HIPAA, PCI-DSS, GDPR, SOC 2, and FedRAMP, among others. A security gap in a Power BI deployment in one of these environments does not just create a support ticket. It creates a breach, a fine, and a reputational incident that can take years to recover from.
This guide covers the security controls that every regulated-industry organisation must configure when deploying Power BI and explains why getting this right requires more than reading the Microsoft documentation. The patterns described here are drawn from AlgoScale’s experience delivering power bi consulting services to financial services, healthcare, and pharma clients across the United States, where our bi consulting firm has built compliance-ready environments that satisfy both internal security teams and external auditors.
Layer 1: Identity and Access Control With Azure Extra ID
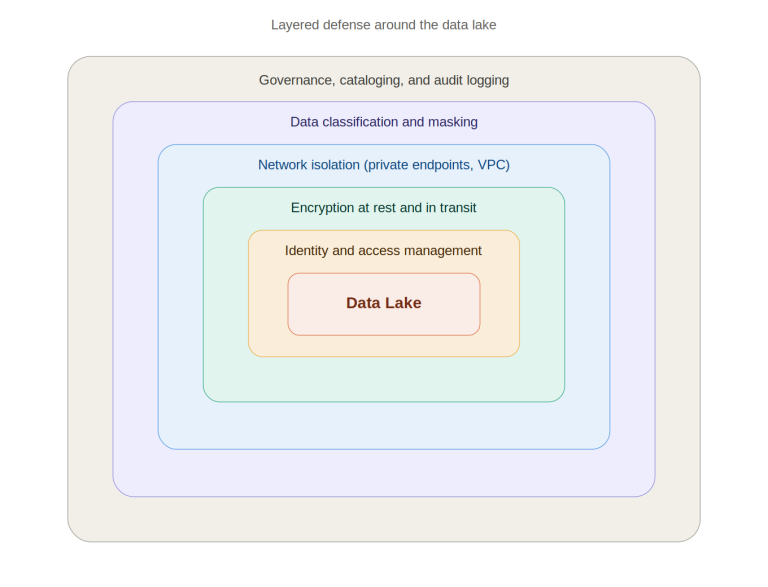
Every Power BI security model begins at the identity layer. Azure Extra ID (formerly Azure Active Directory) provides the authentication backbone for the Power BI service. For regulated industries, this means enforcing Multi-Factor Authentication for all users who can access sensitive datasets, no exceptions. Conditional Access policies should restrict Power BI access to compliant, managed devices and block logins from unexpected geographies. Single Sign-On eliminates password sprawl and ensures that when an employee is offboarded, their access to every connected service is revoked immediately through a single identity lifecycle event rather than requiring manual cleanup across multiple systems. A bi consultant working in regulated environments treats Entra ID configuration as the first task on every engagement because every subsequent security control depends on it.
Layer 2: Row-Level Security and Object-Level Security
Row-Level Security (RLS) restricts the rows of data that a specific user sees within a Power BI report, based on their identity. In a healthcare setting, this means a department head sees patient records only for their department. In a financial institution, a regional manager sees P&L data only for their region. RLS must be designed into the data model not applied as a report-level filter, which can be bypassed by anyone who can export to Excel or access the underlying dataset directly.
Object-Level Security (OLS) extends this concept to columns and tables. If a dataset contains a salary column that should only be visible to HR leadership, OLS removes it from the model entirely for users without the appropriate role; they cannot see the column in field lists, cannot write DAX against it, and cannot observe it through any report interaction. Both RLS and OLS should be implemented using dynamic patterns that reference the authenticated user’s identity at query time, rather than static role assignments that must be manually updated when staff change roles. AlgoScale’s power bi consulting team builds dynamic security templates that scale across hundreds of users without administrative overhead.

Layer 3: Network Isolation and Private Connectivity
For organisations that cannot allow their analytics traffic to traverse the public internet, Power BI supports Private Endpoints that route all data plane traffic through Azure Private Link. This means the Power BI service communicates with data sources over a private network path that is invisible to the public internet. Combined with Virtual Network data gateways, which allow Power BI to connect to on-premises or Azure-based data sources without opening inbound firewall ports, this creates a network architecture that satisfies the most demanding security teams. IP allowlisting at the gateway level adds a further control point, restricting which IP ranges can initiate gateway communication.
Table 1: Power BI Security Controls by Compliance Framework
| Compliance Standard | Key Requirement | Power BI Control | Additional Step Required |
| HIPAA / HITECH | PHI access restriction | Dynamic RLS + OLS on PHI columns | BAA with Microsoft; audit log review process |
| PCI-DSS | Cardholder data isolation | Workspace segmentation + Private Endpoints | Network segmentation review; QSA sign-off |
| GDPR | Data residency + right to erasure | Capacity in EU region; Purview data map | Deletion workflow; DPO documentation |
| SOC 2 Type II | Continuous controls evidence | Entra ID Conditional Access + audit logs | Log export to SIEM; quarterly evidence pull |
| FedRAMP Moderate | US government cloud boundary | Power BI Government Community Cloud (GCC) | Authority to Operate (ATO) documentation |
| FINRA / SEC 17a-4 | Immutable record retention | Power BI audit log + Purview retention policies | Immutable storage for log exports; eDiscovery |
Layer 4: Data Protection With Microsoft Purview Sensitivity Labels
Microsoft Purview Information Protection integrates directly with Power BI to apply sensitivity labels at the dataset, report, and export level. When a user exports a report containing data classified as Confidential, Purview automatically applies the corresponding label to the exported file which means the file is encrypted and carries access restrictions as it moves outside the Power BI service. This closes one of the most common data leakage paths in BI environments: the Excel export. Configuring Purview sensitivity labels, mapping them to Power BI datasets, and enforcing export restrictions requires coordination between the security team, the data governance team, and the power bi consulting team. AlgoScale handles this integration as part of every regulated-industry deployment.
Layer 5: Audit Logging, Monitoring, and Incident Response
Compliance is not just about preventing unauthorised access it is about being able to prove that access controls were in place and functioning when an auditor asks. The Power BI Activity API logs every user action: who viewed which report, who exported data, who changed a dataset’s permissions, who deleted a workspace. These logs must be exported to a SIEM or long-term storage on a scheduled basis, because the Power BI service only retains activity data for 90 days. A business intelligence consulting engagement for a regulated client always includes a log export pipeline, an alerting rule for anomalous activity (such as bulk exports at unusual hours), and a documented incident response procedure that defines what to do when an alert fires. Without this layer, the other security controls are unverifiable which is the same as not having them at all.

Workspace Architecture for Tenant Isolation
In multi-department or multi-entity organisations, workspace structure is a governance and security decision, not just an organisational convenience. Content that belongs to one business unit should not be visible to another unless explicitly shared. Separate workspaces, each with their own access control lists, prevent accidental exposure. Premium capacity assignment at the workspace level isolates compute resources and prevents one team’s heavy queries from degrading another’s report performance. Deployment pipelines (Development, Test, Production) create a controlled release process that reduces the risk of untested changes reaching production reports that executives and external auditors rely on. Power bi consulting services that include workspace architecture design save considerable governance headaches later, when the number of workspaces has grown from five to fifty.
Table 2: On-Premises vs Cloud Security Model for Power BI
| Security Dimension | On-Premises / SSRS | Power BI Cloud (Managed by AlgoScale) |
| Authentication | Windows AD / Kerberos | Azure Entra ID + MFA + Conditional Access |
| Data in Transit | TLS (version varies) | TLS 1.3 enforced end-to-end |
| Data at Rest | SQL Server TDE | AES-256 in Azure; Purview sensitivity labels |
| Access Logging | SQL Audit or manual | Power BI Activity API + SIEM integration |
| Row-Level Control | Database-level or view-based | Dynamic RLS + OLS in the semantic model |
| Export Control | No native control | Purview labels restrict export format and destination |
| Compliance Evidence | Manual; spreadsheet-driven | Automated log export; monthly evidence package |
Capacity Isolation and Multi-Tenant Security Design
For organisations that serve multiple clients or business units from a single Power BI tenant, capacity isolation is a critical security and performance control. Power BI Premium capacity can be allocated to specific workspaces, ensuring that one business unit’s heavy reporting workload does not degrade the experience for another. For multi-tenant scenarios where a single Power BI environment serves multiple external clients, each of whom must see only their own data, the architecture requires careful design of both the data model and the security layer.
The recommended approach for multi-tenant scenarios uses a combination of dynamic RLS, service principal authentication for embedded scenarios, and workspace-per-tenant deployment for workloads that require strict compute isolation. A bi consulting firm with embedded analytics experience designs these patterns to be maintainable as the number of tenants grows because a pattern that works for ten tenants often breaks in unexpected ways at one hundred. AlgoScale has built multi-tenant Power BI architectures for US-based SaaS companies and financial services providers where the number of tenants ranges from dozens to thousands, and we apply the patterns that scale reliably across that full range.
Power BI Data Loss Prevention Policies
Microsoft Purview Data Loss Prevention (DLP) policies for Power BI allow administrators to detect and respond to situations where sensitive data in Power BI datasets may be at risk of inappropriate exposure. DLP policies can flag datasets that contain credit card numbers, social security numbers, or other sensitive patterns, and trigger alerts or restriction actions automatically. For regulated industries, DLP policies provide an automated control that reduces the risk of human error. A developer who accidentally publishes a dataset containing PHI to a broadly accessible workspace will trigger a DLP alert before the exposure becomes a reportable incident.
Configuring DLP policies for Power BI requires understanding both the Microsoft Purview policy framework and the specific data patterns that represent risk in your industry. AlgoScale’s power bi consulting security practice includes DLP policy design as a standard deliverable for regulated-industry clients, covering not just the policy configuration but also the response workflow: who gets alerted, what they are expected to do, and how the incident is logged. This operational layer is what makes DLP a real control rather than a checkbox on a security audit.
Training Users on Power BI Security Responsibilities
The most sophisticated technical security controls can be undermined by untrained users. A business user who does not understand sensitivity labels may mark a Confidential dataset as General to avoid restrictions. A report developer who does not understand workspace tiers may publish a draft dataset containing sensitive data to a broadly shared workspace. Security training for Power BI users is not a one-time event; it is an ongoing programme that reinforces key behaviours at the moments when they matter most. AlgoScale delivers security awareness training for Power BI as part of every regulated-industry business intelligence consulting engagement, covering the specific controls that users interact with and the consequences of circumventing them.
Training is structured by role: report consumers learn about sensitivity labels and appropriate export behaviour; report developers learn about workspace tiers, certified dataset usage, and when to request security review; dataset owners learn about RLS/OLS configuration requirements and the certification process. Short, scenario-based training modules thirty minutes per role are far more effective than hour-long general security briefings because they connect the policy to the specific actions the user takes in their daily work. Power bi consulting services that include this user-role-specific training produce environments where the security controls hold in practice, not just in the architecture diagram.
Secure Your Enterprise with AlgoScale’s Power BI Consulting Services
Power BI security is not just about enabling authentication or restricting report access. In regulated industries, it requires a carefully designed framework that combines identity management, role-based access control, data protection, governance, monitoring, and compliance. A single misconfigured permission or unsecured dataset can expose sensitive information, trigger regulatory penalties, and damage customer trust.
At AlgoScale, we help organizations build secure, compliant, and enterprise-ready Power BI environments that align with industry regulations such as HIPAA, PCI-DSS, GDPR, SOC 2, FedRAMP, and FINRA. Our Power BI consultants design security-first architectures using Microsoft Entra ID, Dynamic Row-Level Security (RLS), Object-Level Security (OLS), Microsoft Purview, Private Endpoints, Data Loss Prevention (DLP), audit logging, and automated compliance monitoring to protect your most critical business data.
Whether you’re implementing Power BI for the first time, modernizing an existing deployment, or securing a multi-tenant analytics platform, AlgoScale’s Power BI consulting services deliver scalable, governance-driven solutions that meet both business and compliance requirements.
Partner with AlgoScale to build a secure, compliant, and future-ready Power BI environment that empowers your teams with trusted insights without compromising security or regulatory standards.